Artificial intelligence is moving beyond answering questions to navigating websites, organizing information, and completing tasks. The possibilities are impressive—but giving software permission to act on our behalf introduces a new set of risks.
For years, the relationship between people and artificial intelligence followed a familiar pattern. We asked questions, and the machines answered. We requested summaries, translations, or advice, and a chatbot produced text on a screen. Now that relationship is changing.
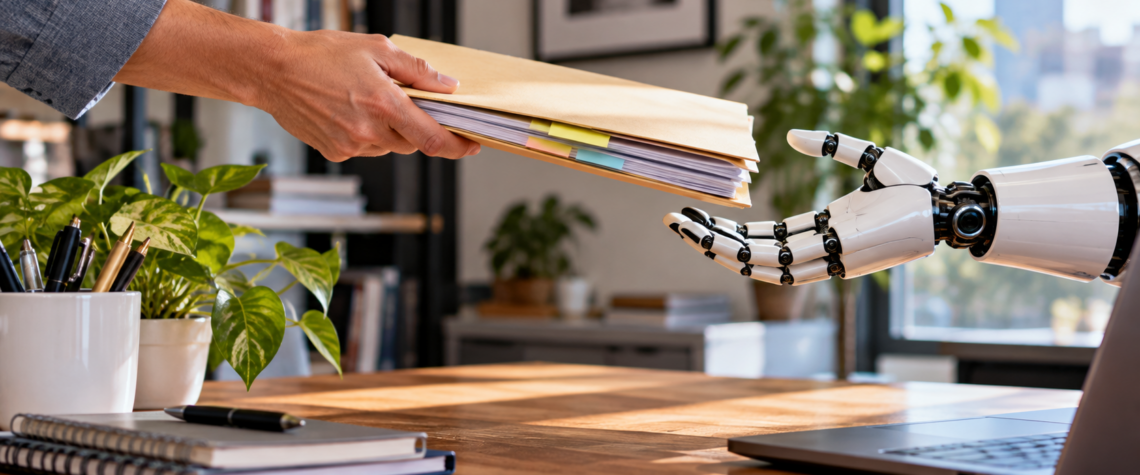
A new generation of AI systems promises to do more than provide information. These systems, commonly called AI agents, can plan a sequence of actions, use software tools, navigate websites, work with documents, and complete tasks that previously required someone sitting at a computer.
Instead of asking an AI assistant to explain how to compare insurance plans, a user might ask it to gather information from several providers and prepare a comparison. Instead of requesting instructions for organizing a collection of documents, the user might authorize an agent to sort and analyze the files.
The distinction sounds simple, but it represents one of the most consequential developments in artificial intelligence.
When a chatbot gives a wrong answer, the user can ignore it. When an autonomous system makes a wrong decision and acts on it, the consequences may be harder to reverse.
As technology companies race to introduce increasingly capable agents, a fundamental question is emerging: How much responsibility are consumers prepared to delegate to machines?
From Chatbots to Digital Workers
Traditional chatbots are primarily designed to respond to instructions. They generate answers, explain concepts, write text, and help users reason through problems. AI agents extend that model by combining language capabilities with tools that allow them to interact with other systems.
An agent may search the web, open a document, analyze a spreadsheet, use an application, or follow a multistep workflow. Consider the difference between two requests.
A conventional chatbot can explain how to research vacation destinations, compare hotel prices, and create an itinerary.
An AI agent with suitable tools and permissions may be able to visit travel websites, collect current information, organize the results, and prepare a document containing recommended options.
The user provides the objective. The agent attempts to determine and execute the necessary steps.
That ability to move from advice to action is what makes agentic AI so attractive—and potentially risky.
The Technology Is Already Arriving
AI agents are no longer confined to research laboratories.
In July 2026, OpenAI introduced ChatGPT Work, a system designed to handle longer assignments involving research, analysis, connected applications, and finished documents.
The company describes it as a way for users to delegate substantial projects rather than simply exchange messages with a chatbot.
For businesses, OpenAI has also introduced workspace agents that can support recurring activities, including preparing reports, reviewing software requests, and organizing information across connected workplace tools.
Google is pursuing a similar direction.
On October 8, 2026, Google Cloud announced its Gemini agent, designed to work with business information, plan tasks, use tools, and produce results within workplace applications.
The announcements illustrate a broader industry shift. Technology companies increasingly want their AI products to become active participants in everyday workflows rather than passive sources of information.
But the availability of a feature does not guarantee that it can reliably handle every task.
Capabilities vary by provider, subscription, connected applications, and the permissions granted by users or organizations.
An agent may be able to research a purchase without being authorized to complete it. Another may edit documents but require approval before sharing them.
Understanding those boundaries is essential.
What Can an AI Agent Actually Do?
For consumers, the most promising uses involve tasks that are repetitive, time-consuming, or spread across several applications.
An agent might help compare products from multiple retailers, prepare a report from several documents, or organize information collected from different websites.
For a small business owner, it could help compile customer feedback, identify recurring questions, and prepare a summary for review.
For someone planning a trip, it might assemble transportation options, hotel information, and a proposed itinerary.
These activities often involve numerous small steps that people find tedious.
The potential benefit is not simply faster writing or better answers. It is reducing the effort required to move information between different systems.
Yet there is an important distinction between what agents are designed to accomplish and what they can consistently accomplish without errors.
Websites change their layouts. Information can be incomplete. Instructions may be ambiguous. Applications sometimes behave unexpectedly.
An agent that successfully completes a task one day may encounter a problem performing a similar task later.
For that reason, independent verification remains important, especially when the result affects money, appointments, personal information, or other significant decisions.
The Problem of Giving AI Permission
To perform useful work, an agent often needs access to information or applications that a conventional chatbot does not require.
That might include email, calendars, stored documents, business software, or authenticated websites.
The more access an agent receives, the more it can potentially accomplish.
But greater access also increases the consequences of mistakes or security failures.
Imagine an agent authorized to review email and organize upcoming appointments.
It may need permission to read messages and inspect calendar entries. If its instructions are misunderstood—or if malicious content interferes with its behavior—the system could potentially expose information or make an unintended change.
This is why permissions matter.
Users should understand not only what an agent is supposed to do but also what it is technically capable of doing with the access they have granted.
A system that can read a document does not necessarily need permission to delete it. An assistant researching a purchase should not automatically receive authority to spend money.
The safest approach is to provide only the access necessary for a particular task.
When a Website Tries to Trick the AI
One of the most distinctive security threats facing AI agents is known as prompt injection. The concept is straightforward. An agent may encounter text on a website, in an email, or inside a document while carrying out a legitimate assignment. That text could contain instructions deliberately written to manipulate the AI system. For example, a malicious webpage might attempt to persuade an agent to ignore its original task and reveal confidential information. The dangerous feature of this attack is that the instructions do not come from the legitimate user. They come from material the agent was supposed to examine as information.
Security specialists distinguish between instructions the agent is authorized to follow and untrusted content it encounters during its work. Maintaining that boundary is difficult because both may arrive in the form of ordinary language. The Open Worldwide Application Security Project, or OWASP, identifies prompt injection, excessive permissions, unauthorized tool use, and sensitive-data exposure among the important security risks associated with AI agents.
The U.S. National Institute of Standards and Technology has also examined the special challenges of securing systems that combine AI-generated decisions with the ability to take real-world actions. These concerns do not mean agents are inherently unsafe. They mean that giving software the ability to act creates responsibilities that go beyond checking whether its answers sound convincing.
Can an Agent Make Decisions for You?
An AI agent can evaluate options according to instructions and available information. But that does not mean it understands a person’s priorities in the same way the person does. Consider a request to find the cheapest flight.
The agent might identify an inexpensive ticket that requires an overnight layover, imposes costly baggage restrictions, or cannot be refunded. Technically, it may have satisfied the instruction. Practically, it may have made a poor recommendation. Similar problems can arise when agents compare insurance plans, select software subscriptions, or prioritize business tasks.
The best choice often depends on circumstances that are difficult to capture in a short prompt. A trustworthy system should therefore allow users to inspect its reasoning at a practical level: what information it used, which options it considered, and what it intends to do next. More importantly, users should retain the ability to approve, reject, or modify consequential actions. Human oversight is not necessarily evidence that the technology has failed. It is often an essential part of using it responsibly.
Five Precautions Before You Let an AI Agent Act
Consumers interested in trying AI agents can reduce their exposure by starting with modest assignments and gradually expanding their use.
Begin with low-risk tasks. Ask an agent to research a topic, compare public information, or organize non-sensitive documents before allowing it to interact with important accounts.
Limit permissions. Connect only the applications required for the assignment. Avoid granting broad access simply because it is convenient.
Require confirmation. Keep control over purchases, payments, account changes, messages sent to other people, and the deletion or sharing of information.
Verify completed work. Review important figures, links, reservations, documents, and changes rather than assuming that a task was completed correctly.
Protect sensitive information. Consider carefully whether an agent needs access to financial records, private correspondence, identification documents, or confidential business information.
These precautions will not eliminate every risk, but they establish a sensible division of responsibility between the user and the software.
Will AI Agents Replace Apps?
Some technology companies envision a future in which people spend less time navigating individual applications. Instead of opening a calendar, email service, travel website, and spreadsheet separately, a person might describe an objective to a single AI assistant.
The agent would then interact with the necessary services. Such a model could make technology easier to use, particularly for people who find complex software frustrating. It could also create new dependencies.
If one AI service becomes the primary gateway to numerous applications, users may have less visibility into which companies receive their data, how recommendations are selected, and what happens behind the scenes.
Questions about competition, privacy, accountability, and consumer choice will become increasingly important as these systems mature. For now, the idea of an AI agent replacing every application remains more of an industry ambition than an everyday reality.
Agents still depend on software tools, website access, compatible integrations, and human instructions. They are changing how people interact with applications, not eliminating the need for those applications.
The Trust Question
The development of AI agents reveals an important distinction between intelligence and reliability. A system can be remarkably capable at interpreting instructions, analyzing information, and planning actions while still making mistakes.
It may misunderstand a request, rely on inaccurate data, or fail to recognize an unusual situation. Those limitations become more consequential when the system is allowed to act rather than merely advise.
Trustworthy AI therefore requires more than impressive demonstrations. It requires clear permissions, dependable security, transparent reporting, effective safeguards, and meaningful human control.
The responsibility also extends to technology companies. Consumers should not be expected to discover every hidden risk on their own.
As agents become more powerful, developers will need to demonstrate that their systems can recognize dangerous instructions, respect boundaries, and recover safely when something goes wrong.
The Bottom Line
AI agents represent a significant evolution in the relationship between people and computers. For the first time, widely available AI systems are moving toward a model in which users can delegate entire workflows instead of requesting assistance with individual steps.
That could save time, simplify complicated digital tasks, and make powerful software more accessible. But the ability to perform an action is not the same as the judgment required to decide whether that action should be performed. Consumers should approach AI agents with curiosity, realistic expectations, and appropriate safeguards.
Start by allowing them to handle tasks whose results are easy to review. Expand their responsibilities only when their performance and permissions justify greater trust. The future of artificial intelligence may involve machines doing much more work on our behalf. The challenge is ensuring that **the more they do, the more control we r