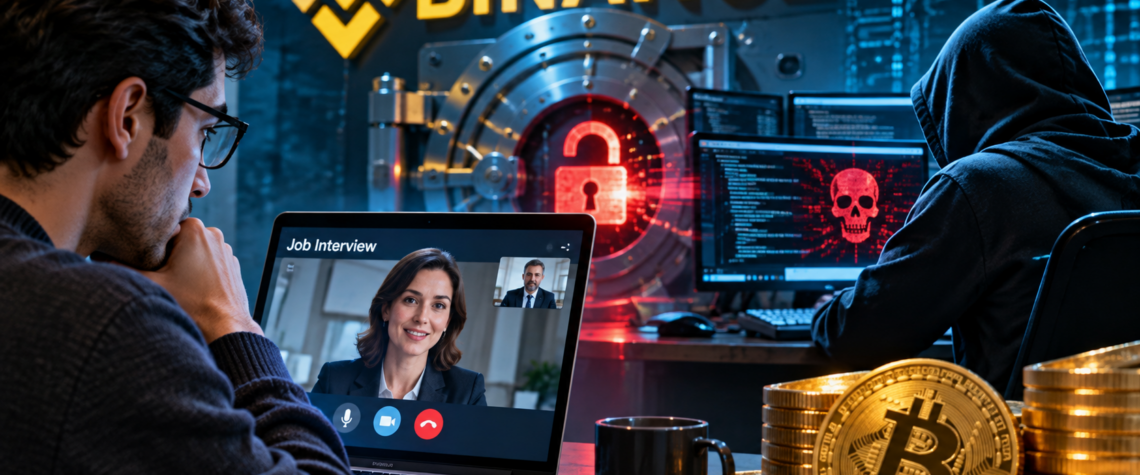
The massive Binance cryptocurrency heist began with malicious software and a convincing recruitment scam. Months later, attackers exploited an internal AI tool to reach the systems protecting billions of dollars in digital assets.
It began with what appeared to be an ordinary opportunity for a software engineer: an invitation to interview for a new job. There was a recruiter, a video interview, a company executive, and eventually a programming assignment.
The company was fictitious. The assignment contained malicious software. And the employee worked for Binance, the world’s largest cryptocurrency exchange.
Weeks later, hackers had stolen approximately $6.34 billion in digital assets from the company, in what may be the largest cryptocurrency theft ever recorded.
According to an initial investigation released by Binance on November 3, the October 29 attack was the culmination of a sophisticated operation that began months earlier and combined psychological manipulation, malware, stolen credentials, and the compromise of an internal artificial intelligence tool.
The FBI has attributed the theft to a North Korean hacking operation associated with the Lazarus Group. North Korea has denied responsibility.
The incident illustrates a troubling reality of modern cybersecurity: even companies operating some of the world’s most valuable digital financial systems can be compromised through the computers and everyday activities of their employees.
The First Breach Came Months Earlier
Binance says the attackers first gained useful information in June, when an engineer inadvertently downloaded a compromised software installation package while setting up a development tool.
The company’s security team detected the suspicious activity, replaced the affected computer, and changed potentially exposed credentials.
But the attackers had already learned something valuable: the engineer’s role within Binance and the identities of colleagues responsible for its cryptocurrency wallet infrastructure. That information helped them identify their next target.
In September, another Binance engineer was contacted through a legitimate employment platform by someone claiming to represent a technology company.
The supposed recruiter arranged a video interview with a human resources representative. To establish credibility, the interviewer shared a social media profile containing photographs and videos.
A second interview followed, this time with someone posing as the company’s chief executive.
Near the end of the conversation, the engineer was instructed to download a programming assignment from an online code repository.
Such assignments are common in software recruitment. Applicants are frequently asked to examine code, complete a technical challenge, or demonstrate their programming skills. But this assignment contained malware.
When the engineer ran the code on a work computer, the attackers gained a foothold inside Binance’s systems. According to the company’s account, the malicious program replaced a legitimate software component, established communication with an external server controlled by the attackers, and concealed evidence of its activities. The company’s endpoint security software did not initially detect the intrusion.
How an Internal AI Tool Became Part of the Attack
The hackers did not immediately steal the money. Instead, they continued moving through Binance’s infrastructure.
On October 20, according to the company’s preliminary findings, the attackers used the compromised engineer’s computer and an internal AI tool to gain access to two additional employees’ systems.
These employees worked on the infrastructure supporting Binance’s cryptocurrency wallets. The attackers obtained credentials and permissions that eventually allowed them to reach critical wallet systems.
This is one of the most significant aspects of the case. Artificial intelligence was not necessarily the mastermind behind the robbery. Binance has not established that an AI system independently planned or executed the operation.
Rather, the attackers reportedly exploited an internal AI tool as part of their efforts to expand access inside the organization. The distinction matters. As businesses integrate AI assistants into programming, administration, research, and internal operations, those tools may become additional pathways through which compromised users or attackers can access sensitive information and systems.
An AI assistant with broad access privileges may become particularly valuable to an intruder who has already stolen an employee’s credentials. The Binance case raises urgent questions about how companies secure internal AI systems, restrict their permissions, and monitor their use.
The $6.3 Billion Theft
On October 29, the attackers used stolen credentials and compromised infrastructure to execute malicious transactions involving Binance’s cryptocurrency wallets.
The company says the theft involved multiple cryptocurrencies and blockchain networks. In one phase, attackers transferred more than 233 million XRP tokens from five internet-connected wallets in approximately four minutes.
Binance detected suspicious transfers and began attempting to freeze assets and stop further unauthorized transactions. But the attackers had exploited transaction-authorization mechanisms that complicated the response, allowing additional transfers while the company worked to revoke compromised permissions. By the time the operation ended, approximately $6.34 billion in digital assets had been removed from affected wallets.
Binance reported on November 3 that approximately $2.85 billion had been frozen or intercepted. The company also said it had replenished 98 percent of affected token assets as of October 31 and committed to covering customer losses. Those figures describe the company’s reported recovery and reimbursement efforts, not a determination that all stolen assets have been recovered.
Binance says it has rebuilt affected systems, replaced compromised devices, revoked exposed credentials, and commissioned an independent cybersecurity review.
Why Fake Job Interviews Are Becoming a Cybersecurity Threat
The recruitment scam used against Binance was not an isolated invention.
Security researchers have documented campaigns in which attackers impersonate recruiters, employers, or job applicants to infiltrate organizations. Software engineers are especially attractive targets because their work frequently requires downloading development tools, running unfamiliar code, and accessing sensitive technical systems. An attacker posing as a prospective employer can exploit those ordinary professional activities.
The danger is not necessarily an obviously suspicious attachment or a poorly written email. A malicious interview process may include convincing video calls, professional profiles, multiple conversations, and technical assignments that resemble legitimate recruitment procedures.
The Binance incident demonstrates how such deception can form one stage of a much larger operation. It also illustrates why traditional cybersecurity defenses cannot depend entirely on employees recognizing fraudulent messages. A convincing social engineering attack can defeat human judgment, while sophisticated malware may evade automated detection.
Organizations need security controls that limit the damage even after an employee’s computer has been compromised.
What Workers and Companies Can Learn
For software developers and other professionals, an unexpected recruitment opportunity should not automatically be treated as suspicious. But it should be independently verified before downloading or running unfamiliar software.
Candidates should confirm that recruiters actually represent the companies they claim to work for, examine the origins of programming assignments, and avoid executing untrusted code on employer-managed computers.
When a technical test requires unfamiliar software, a properly isolated environment can reduce the risk. Employees should also follow their organizations’ security policies before using company equipment for outside interviews.
For businesses, the lessons go further. Sensitive credentials should be protected by strong access controls, and permissions should be limited to what employees and automated tools actually need.
Development environments, cryptocurrency signing systems, and internal AI tools require particularly careful monitoring.
Organizations should assume that sophisticated attackers may eventually compromise an individual computer and design their defenses to prevent that incident from spreading into critical systems.
AI assistants deserve the same scrutiny as other privileged software. Their ability to retrieve information, interact with development tools, or perform actions should be tightly controlled and auditable.
The Human Weakness Behind a Technological Crime
The scale of the Binance theft makes it exceptional. But the basic method is familiar. The attackers did not begin by defeating an entire financial platform through a single extraordinary technical breakthrough. They gathered information, identified employees, established trust, installed malicious software, and gradually expanded their access.
Artificial intelligence became part of the attack, but human deception remained central to its success. That combination may become increasingly important as AI tools gain deeper access to corporate systems.
The lesson extends beyond cryptocurrency exchanges. Banks, hospitals, universities, government agencies, and ordinary businesses all rely on employees whose computers and credentials can become gateways to sensitive infrastructure. The Binance case is a reminder that cybersecurity is no longer simply about protecting networks from malicious code.
It is also about protecting the relationships, decisions, and increasingly intelligent tools through which people conduct their everyday work.
A fake job interview opened the door. Malware kept it open. And compromised digital systems allowed the attackers to walk away with billions.
Sources
- Reuters, November 3, 2026 — Binance’s account of the fake recruitment scheme and cryptocurrency theft.
- The Guardian, November 3, 2026 — Reporting on the malware, internal AI tool, and North Korean attribution.
- BleepingComputer, November 3, 2026 — Technical analysis of the compromised development environment and wallet infrastructure.
- The Register, November 3, 2026 — Analysis of the attack sequence and security implications.
- Binance, November 3, 2026 — Preliminary incident investigation and recovery updates.