Researchers uncover Volta-Autodoxer, malicious software designed to steal passwords, financial information, and digital records—then use artificial intelligence to profile its victims.
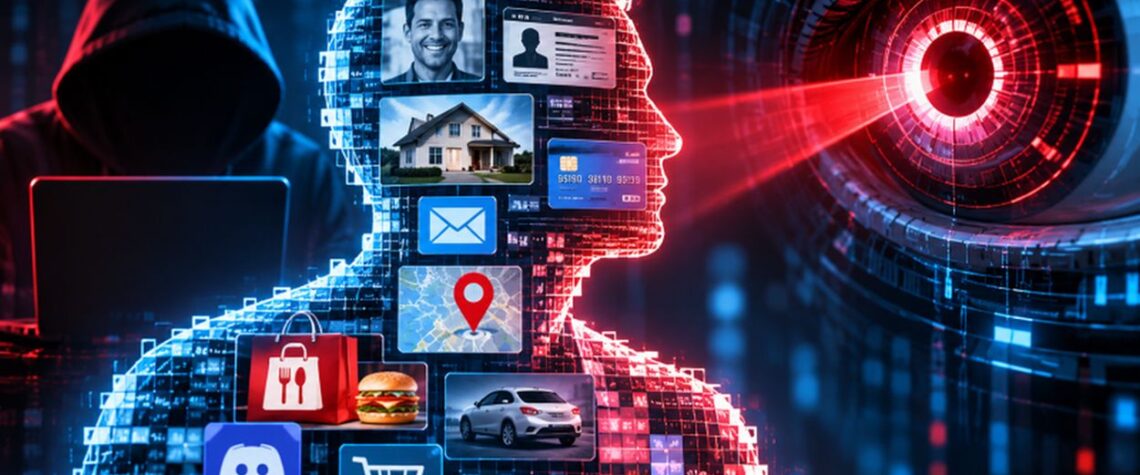
Imagine a criminal gaining access to your computer and stealing your passwords, credit card information, and private messages. Now imagine that criminal using artificial intelligence to analyze everything, determine where you live, estimate your financial worth, and identify which of your accounts would be most valuable to exploit.
That is the disturbing capability researchers have discovered in a new type of information-stealing malware called Volta-Autodoxer.
Identified by cybersecurity researchers at Cisco Talos and reported by WIRED, the malicious software combines conventional data theft with artificial intelligence to create detailed assessments of potential victims.
The discovery illustrates a new development in cybercrime: AI is not necessarily being used to break into computers, but to make stolen information more useful to criminals.
From Stealing Passwords to Building Personal Profiles
Traditional information-stealing malware, often called an infostealer, searches infected computers for valuable information. This can include saved passwords, browser cookies, payment card details, cryptocurrency credentials, and authentication tokens.
Volta-Autodoxer goes further. According to researchers, the malware is designed to collect information from services including Discord, Telegram, Steam, and Roblox. It can also search email accounts and examine records from food-delivery services such as Uber Eats and DoorDash.
Why would criminals care about your dinner orders? Because an ordinary delivery receipt may reveal your name, address, telephone number, spending habits, and frequently visited locations.
When combined with other stolen records, seemingly insignificant details can become part of a surprisingly comprehensive personal profile.
Artificial Intelligence Becomes the Criminal’s Analyst
The most unusual feature of Volta-Autodoxer is what happens after the information has been collected.
Rather than requiring criminals to examine thousands of stolen files manually, the malware can organize the information and submit it to commercial AI models for analysis.
Researchers found that the software uses OpenRouter, a service that connects applications to multiple AI providers. Its configuration includes Anthropic’s Claude, Moonshot AI’s Kimi, and Google’s Gemini.
The AI is instructed to behave like an intelligence analyst, examining the available evidence and producing an assessment of the victim.
That assessment may include the person’s activities, financial value, and security weaknesses.
The malware can also help criminals identify which victims or stolen accounts deserve immediate attention.
In other words, AI becomes a tool for sorting, interpreting, and prioritizing stolen information.
Importantly, the discovery does not mean the AI companies created the malware or authorized its use. Their models are being targeted for misuse through external software.
What Does ‘Autodoxing’ Mean?
The name Volta-Autodoxer refers to the automated creation of personal dossiers.
Doxing traditionally involves collecting and exposing identifying information about someone, sometimes to facilitate harassment, intimidation, or other malicious activity.
Autodoxing extends that concept by using software to gather and connect information automatically.
With AI, the process can become more sophisticated. A model can recognize relationships between apparently unrelated records, identify patterns, and summarize a person’s digital life.
For example, an email receipt may reveal an address, while an account record provides a username and a saved password reveals poor security practices.
Individually, these details may appear unimportant. Together, they can help an attacker understand a victim’s identity, habits, and vulnerabilities.
Has the Malware Already Attacked People?
That remains an important unanswered question. Cisco Talos researchers identified and analyzed the malware, but they have not confirmed whether it has been deployed in active attacks.
The distinction matters. Discovering malicious software demonstrates that a capability exists, but it does not establish how widely criminals have used it.
Researchers nevertheless warn that the technology could make sophisticated targeting techniques available to criminals with relatively limited technical expertise.
The AI component is also optional. Even without access to an AI model, the underlying software retains conventional information-stealing capabilities.
How to Protect Yourself
The discovery offers a reminder that cybersecurity is no longer just about protecting individual passwords. It is also about limiting how much information criminals can collect and combine.
Several precautions can reduce the risks associated with information-stealing malware.
Be cautious when downloading software. Malicious programs are frequently disguised as legitimate applications, free utilities, game modifications, or pirated software. Download programs from trusted sources and avoid unexpected installation files.
Keep your computer and security software updated. Operating-system updates, browser security improvements, and reputable malware protection can help prevent or detect infections.
Use unique passwords and multifactor authentication. A password manager can help generate strong, different passwords for every account. Where available, passkeys or phishing-resistant authentication provide additional protection.
Protect your email account especially carefully. Email often serves as the gateway to password resets, purchase histories, financial notifications, and other personal information.
Review active sessions. If you suspect an infection, use a trusted, clean device to change important passwords, revoke active sessions, and review account activity. Changing a password alone may not invalidate every stolen authentication token.
Monitor financial accounts. Review transactions and enable alerts for unusual purchases or account activity.
No single precaution guarantees protection, but layered security measures can substantially reduce exposure.
A New Chapter in AI-Powered Cybercrime
Volta-Autodoxer illustrates how artificial intelligence can enhance familiar forms of cybercrime without fundamentally changing the way malware enters a computer.
The theft of passwords and personal information is not new. What is changing is the ability to analyze enormous amounts of stolen data quickly and identify valuable targets.
For criminals, this could reduce the time and effort required to exploit compromised accounts.
For everyone else, it reinforces an increasingly important reality: protecting personal information means protecting not only individual pieces of data, but also the digital connections between them.
In the age of artificial intelligence, even an ordinary receipt can become a valuable piece of someone else’s intelligence report.